You’ve been comparing Jamf and Kandji for three weeks. You pull up the vendor site one more time to confirm a pricing detail, and the company is now called Iru.
That’s not a typo and it’s not a rebrand you can safely ignore. Kandji became Iru in October 2025, and the change reaches past the logo. If you’re choosing between an Apple management platform this year, you need to know what changed before you compare features.
Key Takeaways
- Jamf remains the deep, Apple-only control plane it’s always been.
- Kandji, now Iru, is automation-first and has quietly become a broader platform.
- Both are still strong choices.
- Which one fits depends less on features and more on how your team actually works.
Disclosure: This guide is produced by Unduit, which offers device lifecycle services and integrates with both Jamf and Iru.
The Quick Answer
Choose Jamf if:
- Your fleet is Apple-heavy and 500+ devices
- You have a dedicated Mac admin comfortable with scripting and custom policy
- You need deep, granular control and don’t mind building it yourself
Choose Iru (formerly Kandji) if:
- Your team is lean and wants fast time to value with minimal scripting
- You want security, compliance, and MDM unified on one platform instead of stitched together
- You’re managing a mixed Apple and Windows fleet, or expect to soon
Wait, Kandji Is Now Called Iru
On October 22, 2025, Kandji rebranded as Iru and launched a wider platform built around what it calls the Iru Context Model, a unified layer that tracks users, devices, apps, and policy in one place. Existing Kandji customers weren’t forced into new contracts, and enrolled devices kept working exactly as before. But new signups now land on a six-product platform covering identity, endpoint management, EDR, vulnerability management, and compliance automation, not the Apple-only MDM Kandji used to be.
Jamf changed too, just differently. In January 2026, private equity firm Francisco Partners closed a $2.2 billion take-private acquisition of Jamf, ending its run as a public company. Jamf kept its name, its Minneapolis headquarters, and its product roadmap. The ownership change matters mostly for long-term roadmap planning, not day-to-day admin work.
Bottom line: if a blog post, forum thread, or vendor deck you’re reading still talks about “Kandji” without mentioning Iru, treat the rest of its information as dated too.
Jamf vs Kandji (Iru): How They Actually Compare
Deployment and onboarding
Both support zero-touch enrollment through Apple Business Manager. Jamf’s PreStage enrollment is powerful but expects you to build the configuration yourself. Iru’s Blueprints and Liftoff onboarding flow are designed to get a device from box to work-ready with far less manual setup, which is why Iru is often the faster pick for teams without a dedicated Apple specialist.
Zero-touch only covers company-purchased devices registered in Apple Business Manager. You’ll need manual or User Enrollment for:
- BYOD (employee-owned) devices
- Contractors on personal Macs
- Hardware bought outside Apple Business Manager
Jamf supports account-driven User Enrollment, which separates work data from personal data. Iru handles straightforward manual enrollments well, but teams with heavy BYOD usually find Jamf more flexible.
Admin experience and automation
Jamf: granular control, steeper learning curve
- Admins on TrustRadius often describe Jamf Pro as powerful but heavy to administer without training.
- On r/macsysadmin, recurring frustrations include cost creep as add-ons stack up, uneven support response times, and occasional regressions after updates.
- Many of the same admins still call Jamf one of the most flexible macOS MDMs available. The frustration usually comes from running it, not from what it can do.
Iru: automation over customization
- Pre-built templates and auto-remediation keep devices in their desired state.
- Teams moving from Jamf to Iru commonly report managing larger fleets with fewer admins.
- The trade-off is less depth for niche, highly custom workflows.
Security and compliance
Jamf sells security as separate products with a separate agent. Iru runs MDM and security through one agent, but each security module is still priced separately.
Jamf:
- Jamf Protect is a separate product, separate agent, and separate invoice line.
- Management and security live in different tools.
Iru:
- Endpoint management, EDR, vulnerability management, and compliance run through one agent and one shared data model.
- A security event and a policy violation show up in the same place.
- EDR and vulnerability management can’t be bought on their own. Both require the base Endpoint Management product.
Budgeting tip: Treat Iru as modular pricing with a unified backend, not an all-in-one price.
Pricing
Neither vendor makes this simple, and a wall of prose doesn’t help. Here’s the breakdown by product and module:
Migrating Between Jamf and Kandji (Iru)
Switching is more routine than most IT teams expect. Iru provides a Jamf to Iru migration agent that deploys through your current MDM and re-enrols devices with minimal end-user interaction. IT admins who’ve made the switch report migrating fleets in the 900 to 1,200 device range within a single month using the migration agent. The main effort isn’t the technical cutover; it’s re-mapping any custom Jamf scripts and Extension Attributes to their Iru equivalent.
Choose Jamf If / Choose Iru If
What Neither Platform Manages: The Rest of the Device Lifecycle
Jamf and Iru are excellent at what they’re built for: enrolling, configuring, patching, and securing a device once it’s in someone’s hands. Neither one touches what happens before that device is enrolled or after it stops being useful. Procurement, physical shipping and logistics, hardware repair, and end-of-life recovery all sit outside the MDM layer entirely, and most IT teams end up managing that half of the lifecycle in spreadsheets, email threads, and whatever their MDM’s asset report happens to show.
That’s a different problem than choosing between Jamf and Iru, and it’s the one that determines whether your IT team is still firefighting six months after the MDM decision is made.
Choose Unduit for the Rest of the Device Lifecycle
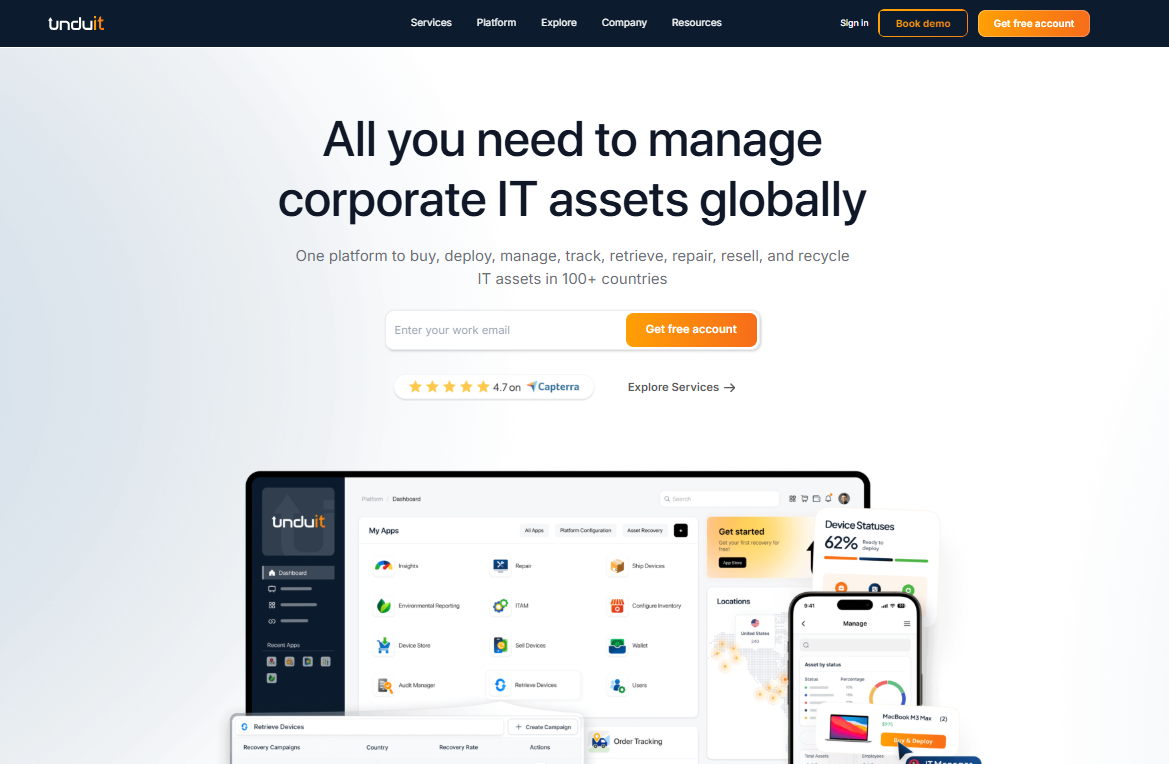
Picking between Jamf and Iru solves the management half of your Apple fleet. Unduit handles the half neither platform touches: procurement, deployment logistics, repair, recovery, and responsible retirement, all from one dashboard your IT team already has visibility into.
Unduit connects natively with both platforms covered in this guide. Jamf and Kandji integrations sync enrollment and inventory data directly into Unduit, so a device’s MDM status and its physical lifecycle status live in the same place instead of two separate systems your team has to cross-reference manually.
That matters most at the edges of the lifecycle, where MDM tools go quiet. When an employee leaves, Unduit’s employee laptop return service takes over where your MDM’s remote wipe command leaves off:
- Automated pickup scheduling that arranges device collection without manual follow-up from your team
- Real-time tracking of every laptop, monitor, and peripheral in transit, from anywhere
- Smart inventory updates that log condition and sync automatically with your asset records
- Refurbish and redeploy recommendations that maximize the value of hardware you already own
- Secure chain of custody, logged and auditable, so compliance teams get the same evidence rigor your MDM gives them for software
- Global support for domestic and international returns without the delays third-party logistics usually add
Your MDM decision and your device lifecycle strategy don’t have to be two separate projects. They work better as one.
FAQs
Q1: Is Kandji now called Iru?
Yes. Kandji rebranded as Iru on October 22, 2025, and expanded from Apple-only MDM into a broader identity, security, and compliance platform.
Q2: Did Jamf get acquired? Is Jamf still independent?
Jamf was taken private by Francisco Partners in a $2.2 billion deal that closed in January 2026. It’s no longer publicly traded but continues operating under the Jamf name.
Q3: Is Iru (Kandji) better than Jamf for small businesses?
Generally yes for lean teams without a dedicated Mac admin, since Iru’s automation reduces the manual configuration Jamf assumes you’ll handle yourself. Larger, Apple-heavy enterprises with complex policy needs tend to lean toward Jamf.
Q4: Can you migrate from Jamf to Iru, or the other way?
Yes. Both platforms support migration tooling, and Jamf-to-Iru moves are the more common and better-documented path.
Q5: Which is better for SOC 2 or ISO 27001 compliance?
Both support these frameworks. Iru bundles compliance templates and continuous monitoring into its core platform, while Jamf handles compliance reporting through its Compliance Benchmarks and Jamf Protect add-on.
Q6: Can Jamf or Iru see what employees do on their Macs?
No, neither is a keylogger. Apple’s MDM framework doesn’t give admins access to keystrokes, messages, email content, or browsing history.